


Rain’s Third Exit in Six Months: Cisco’s $400M Acquisition of Astrix Security
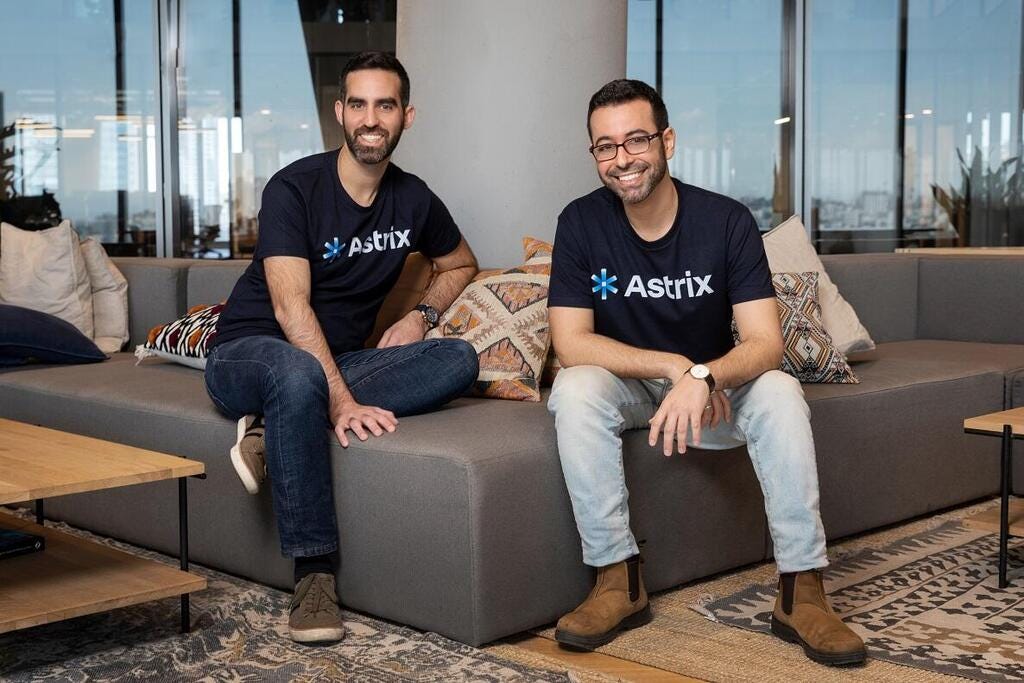
Astrix Security is being acquired by Cisco in a reported ~$400M acquisition, marking Rain Capital’s third exit in six months, following Lakera’s acquisition by Check Point Software Technologies and SPLX’s acquisition by Zscaler.
As enterprises adopt AI agents and autonomous systems, non-human identities are emerging as a critical layer to protect. Astrix built visibility and control for this new category, helping enterprises secure and govern non-human access across agents, APIs, and service accounts across modern enterprise environments.
Cisco plans to integrate Astrix into its broader security and Zero Trust platform, reinforcing the growing importance of identity, access, and runtime control in the AI-native enterprise.
Rain Capital is a seed investor in Astrix and very proud to have witnessed the innovation and growth led by founders Alon Jackson and Idan Gour.
AI Vulnerability Storm: A System-Level Shock
Anthropic’s Mythos release shocked the Cybersecurity industry. The Cloud Security Alliance, together with SANS and OWASP, published a report — “AI Vulnerability Storm” — as a response to Mythos.
LLM models like Mythos that are customized for security tasks represent a step-change in AI-driven vulnerability research — they fundamentally changed the nature of vulnerability discovery and management
Vulnerability discovery moves from scarce to continuous
Exploit generation moves from manual to automated
Time from discovery to exploitation compresses from weeks to hours
As attackers scale with compute while defense remains constrained by patch cycles and coordination, the implication becomes structural. Security teams can no longer rely on a “good enough” security program. This paper outlined a "Mythos-ready" security program built around three priorities: adjusting risk calculations; doubling down on security fundamentals like segmentation, MFA, and defense-in-depth; and immediately deploying LLM-based vulnerability discovery capabilities.
Rain’s Venture Partner Dr. David Brumley Launches ExploitBench
Rain Venture Partner and Carnegie Mellon University Professor Dr. David Brumley, together with Ph.D. student Seunghyun Lee, recently launched ExploitBench, a new benchmark measuring how far AI systems can progress through real-world software exploitation workflows.
Unlike traditional benchmarks focused on vulnerability discovery alone, ExploitBench evaluates the full exploitation ladder — from triggering bugs to achieving arbitrary code execution against hardened production systems.
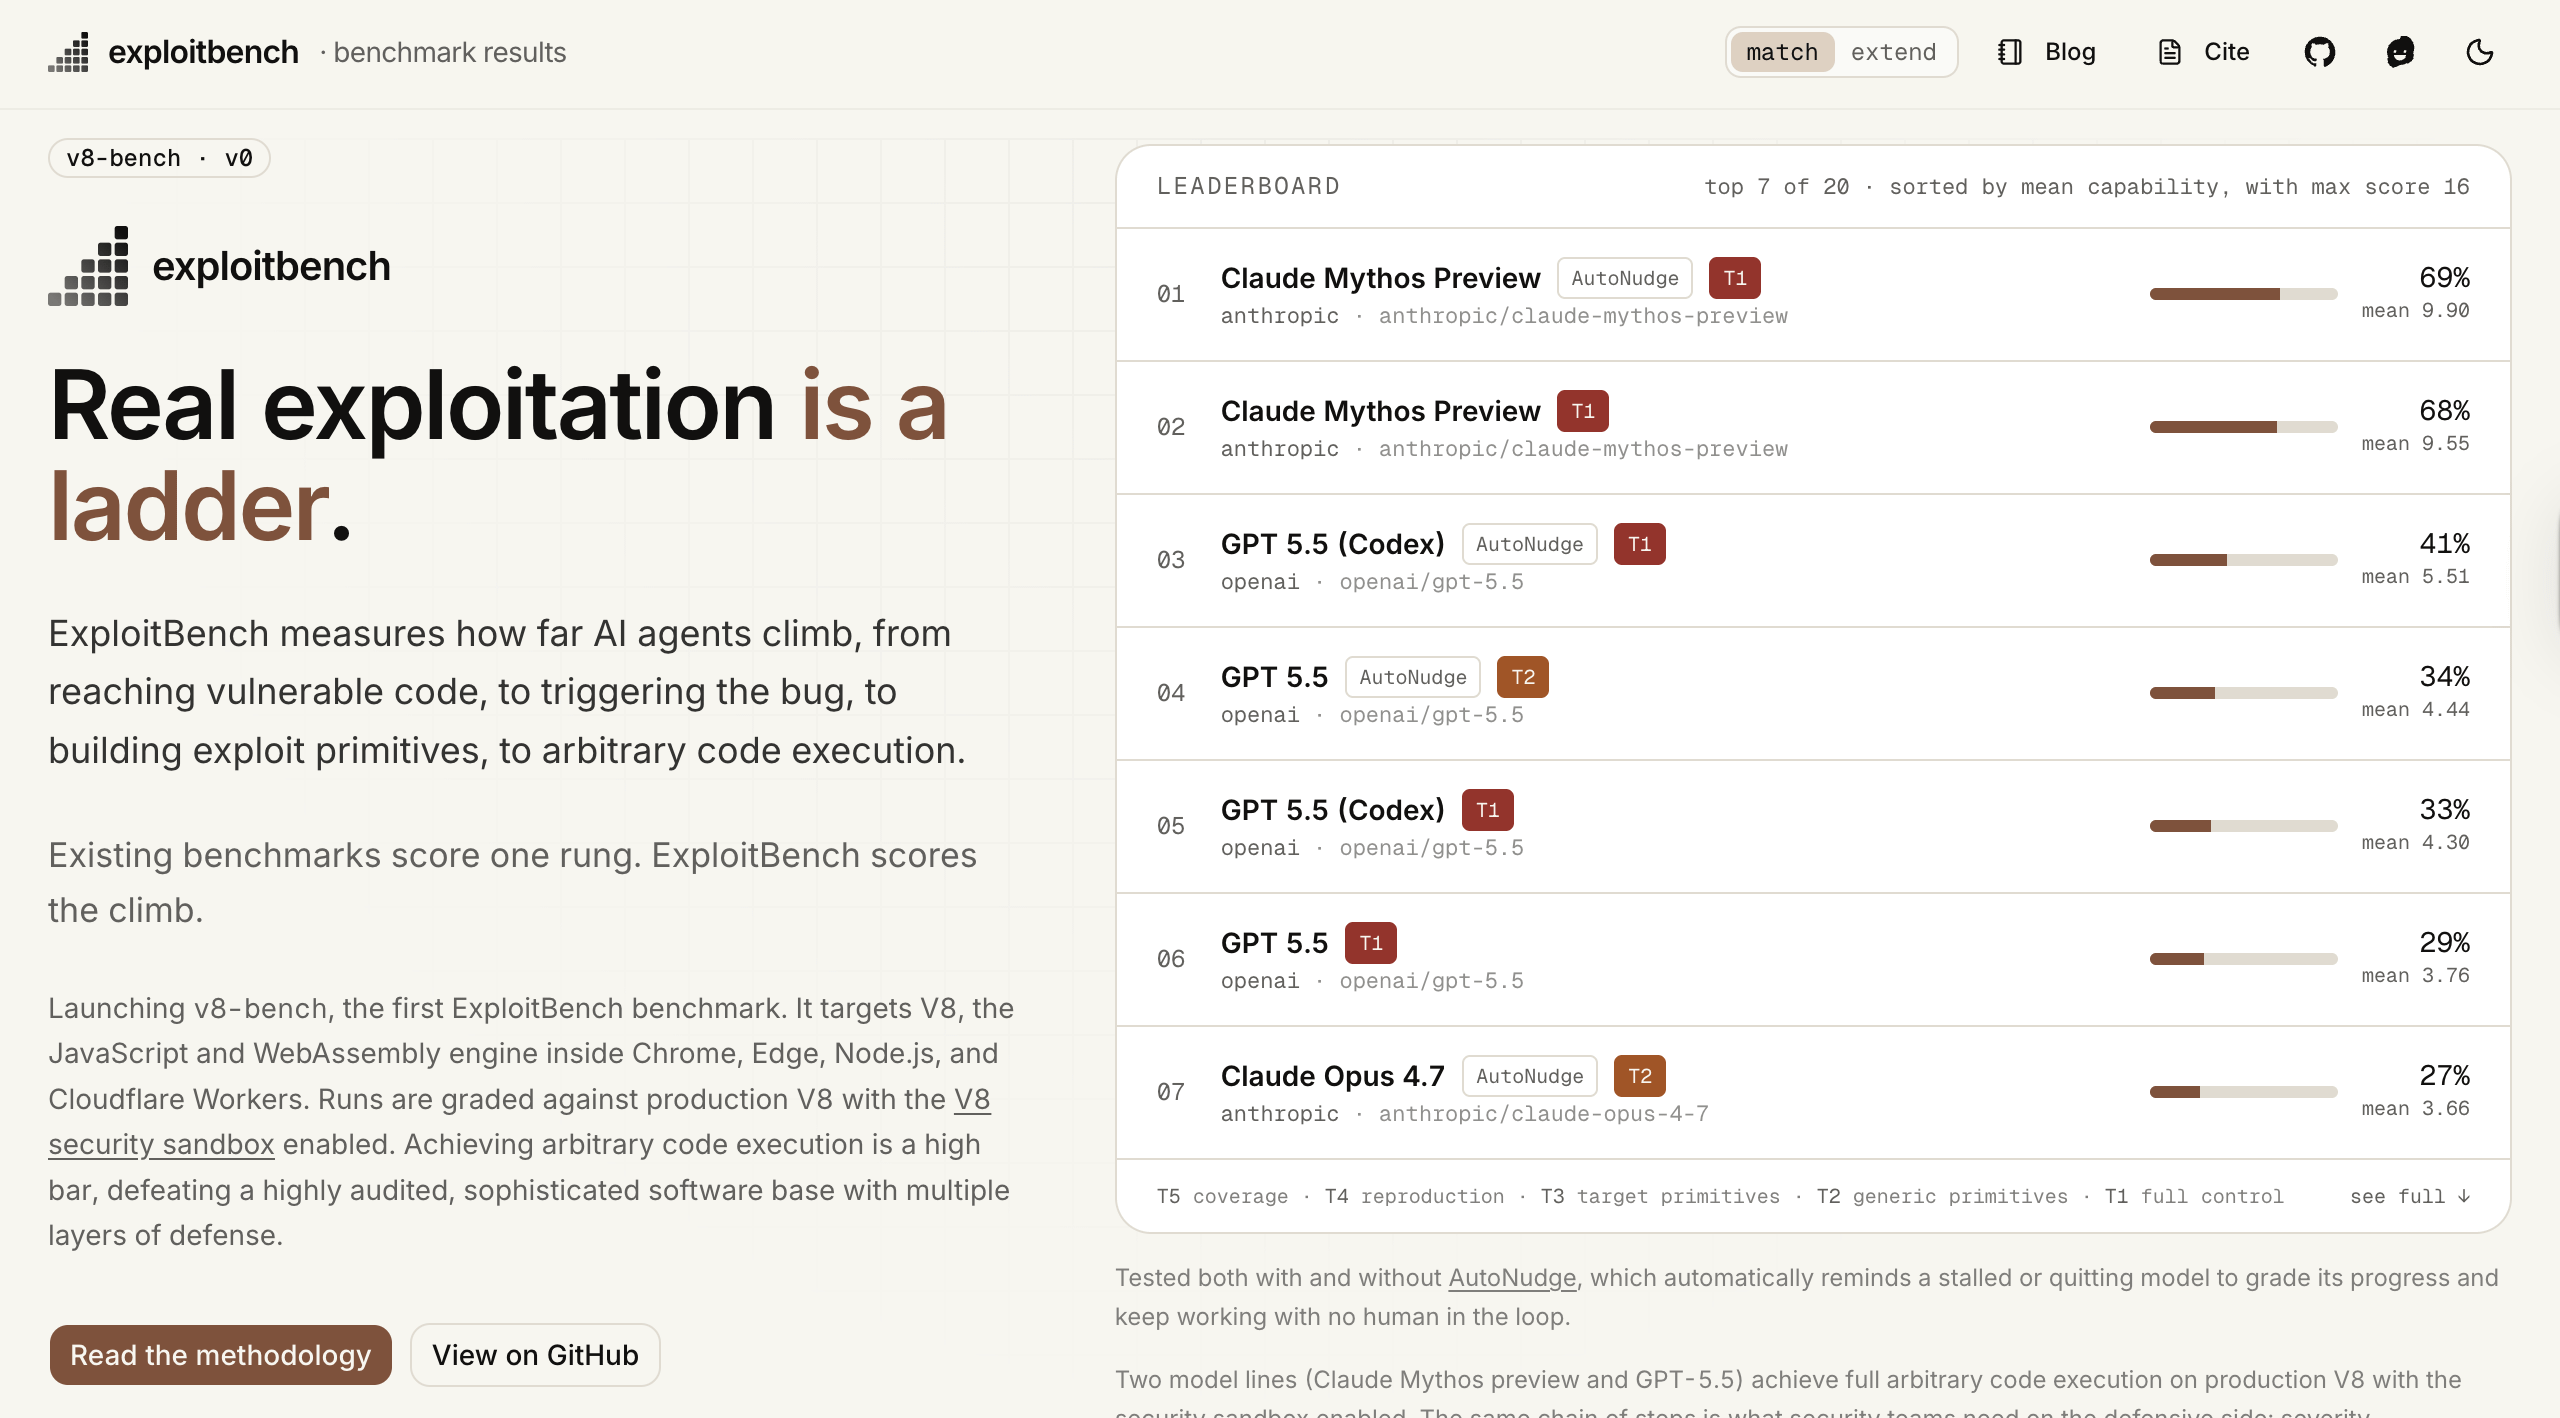
Several findings stood out:
Claude Mythos Preview achieved full arbitrary code execution on 21 of 41 V8 vulnerabilities
GPT-5.5 was the only other model family to reach full ACE capability on selected CVEs
Exploitation performance varied significantly depending on the surrounding agent harness and runtime scaffolding
The takeaway: Autonomous AI systems can execute multi-stage offensive workflows beyond simple detection. We have officially entered the AI exploit era.
When AI Acts: Security and Survival in the Age of Enterprise Agents
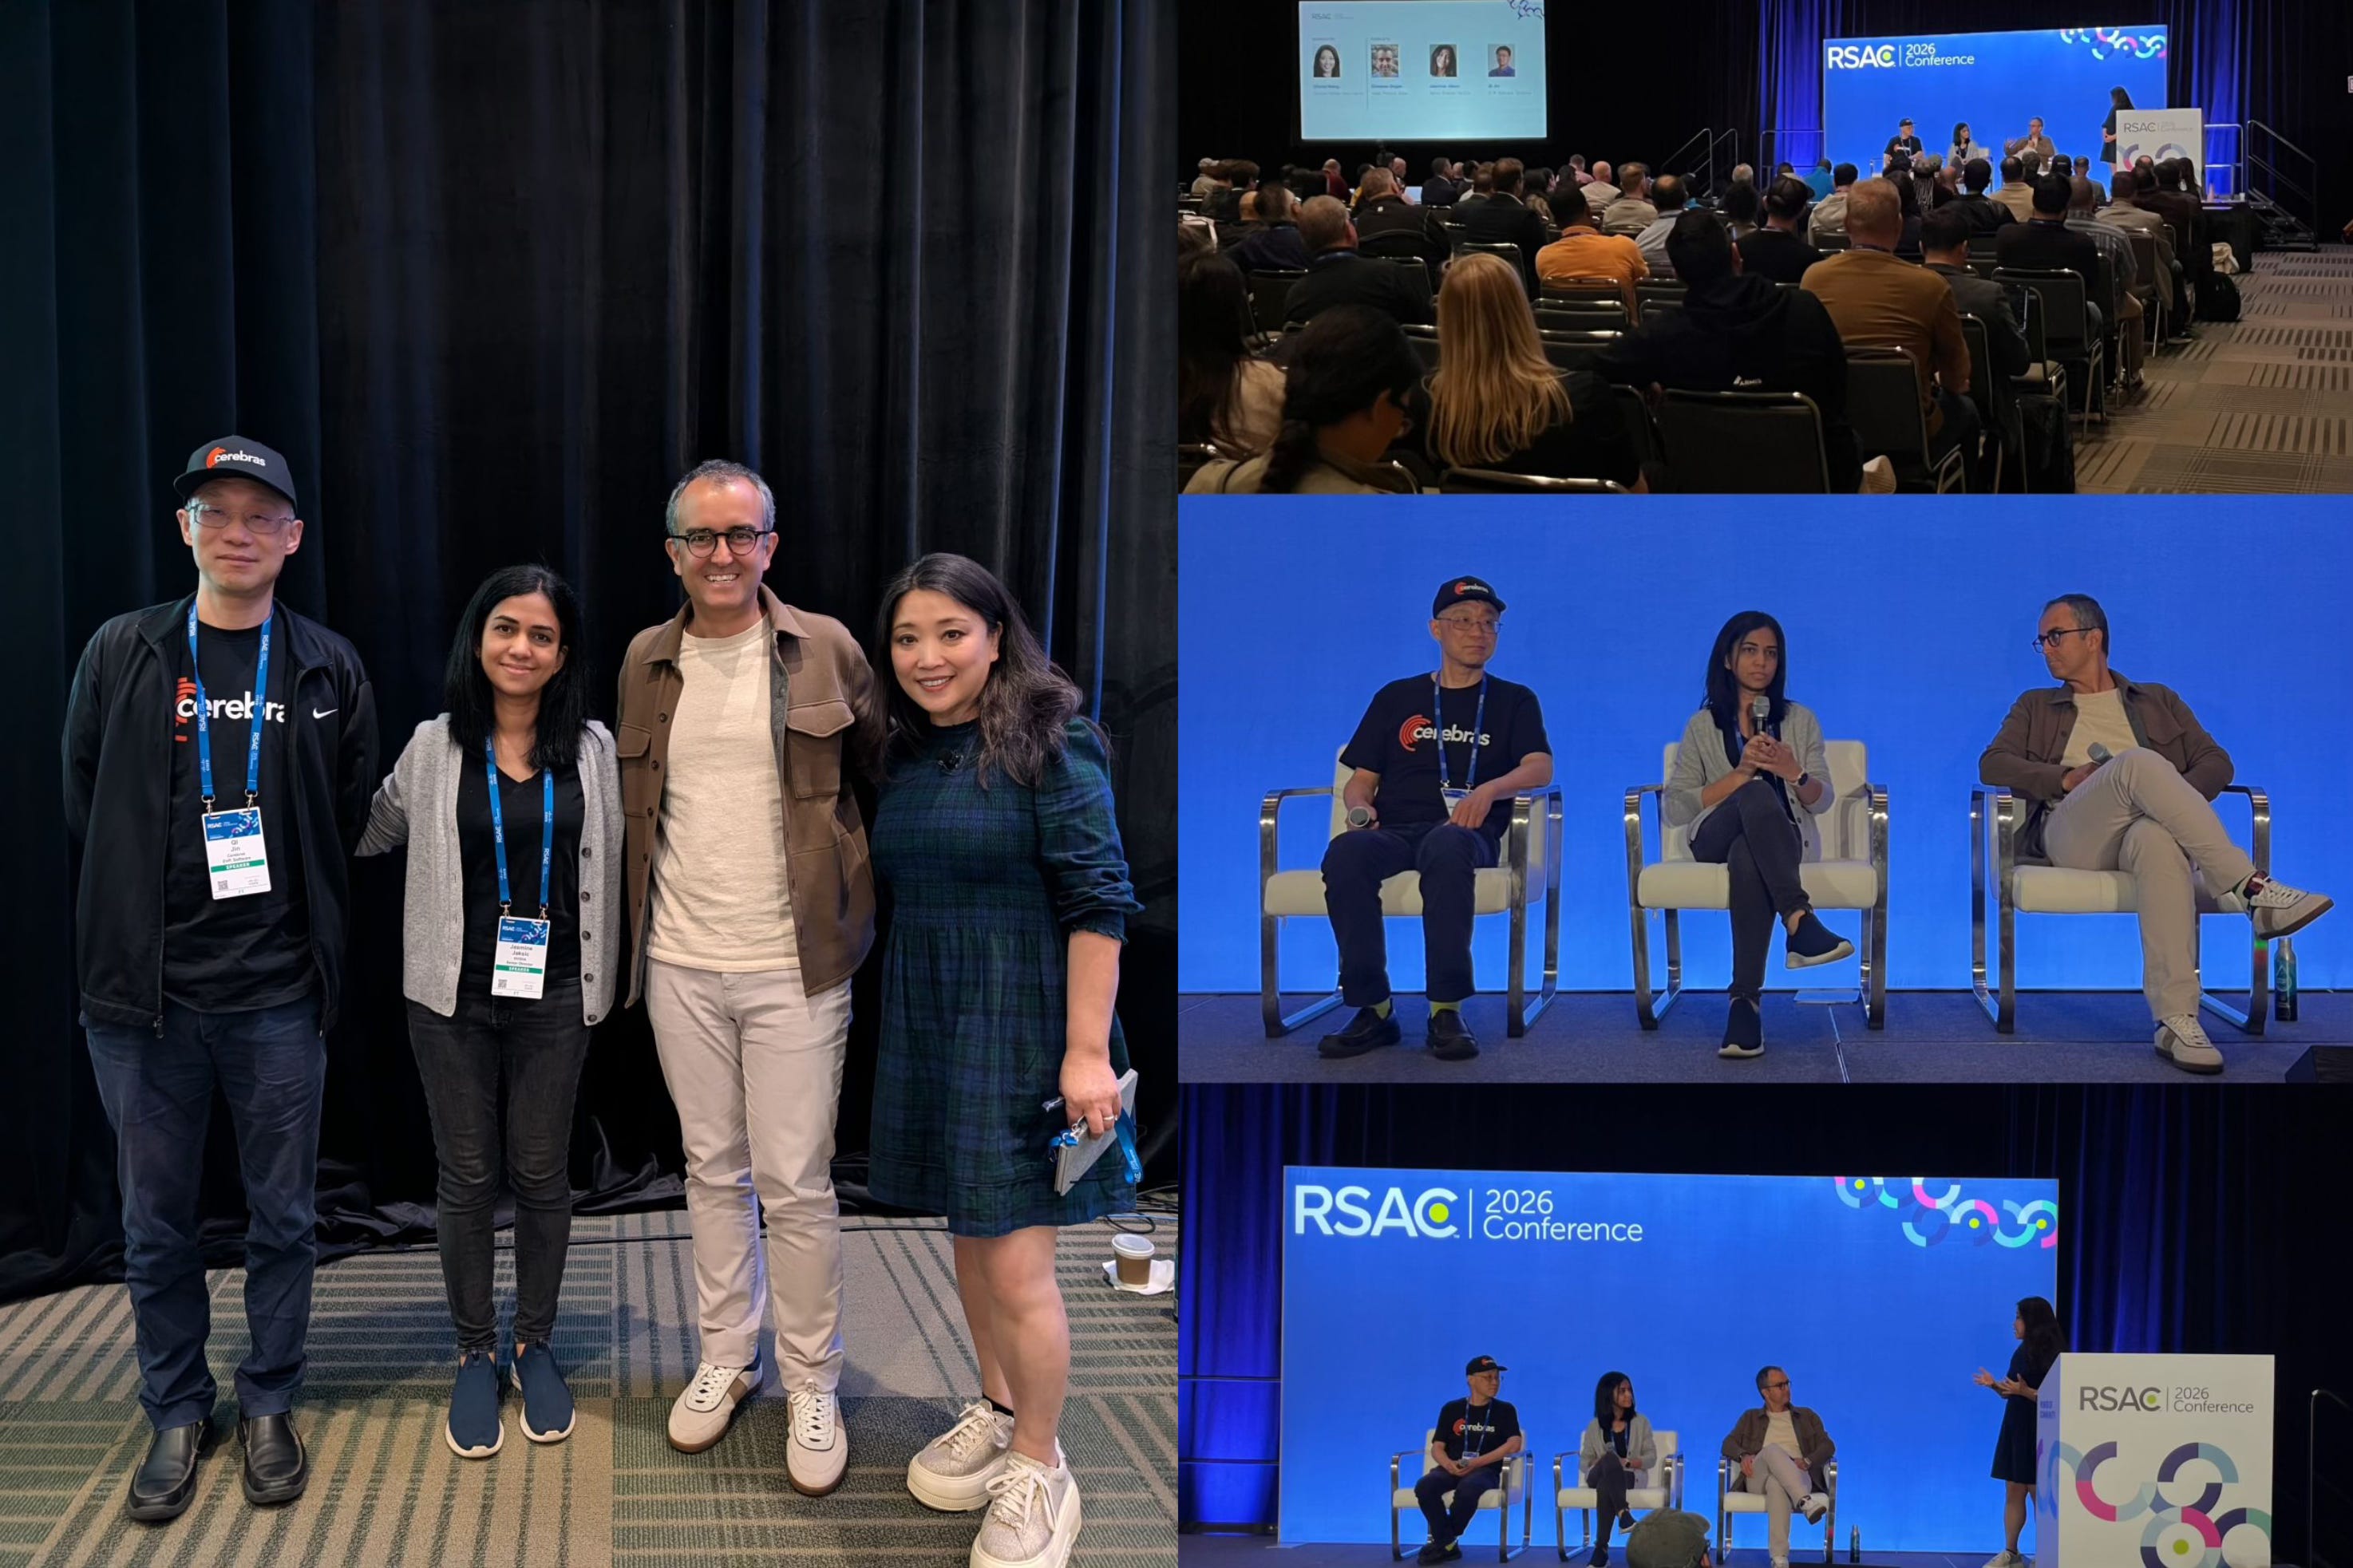
At RSA 2026, Rain Capital’s Founder and General Partner, Dr. Chenxi Wang, joined a panel with Jasmine Jaksic (NVIDIA), Qi Jin (Cerebras), and Emrecan Dogan (Glean) to discuss how agentic AI is moving from experimentation into enterprise production.
A clear theme emerged: as systems become more autonomous, the challenge is no longer just model performance, but how to design for trust, control, and decision-making in production.
Several ideas stood out:
Time-to-decision is becoming a key metric as systems increasingly act in real time
Trust is shifting toward probabilistic outputs, changing how enterprises think about risk and oversight
How to measure success remains an open question beyond traditional model benchmarks
Security is moving to the agent runtime layer, where actions actually happen
The takeaway: Enterprises are decidedly moving from model-centric systems toward decision-driven, agentic architectures
Cybersecurity Funding: A Barbell Market with Rising Execution Risk
At RSA, Our Venture Partner Sidra Ahmed Lefort spoke with ISMG about what’s happening beneath the surface in cybersecurity funding.
While headline numbers remain strong, with over $16B in financing and $80B in M&A, the underlying dynamics are more nuanced.
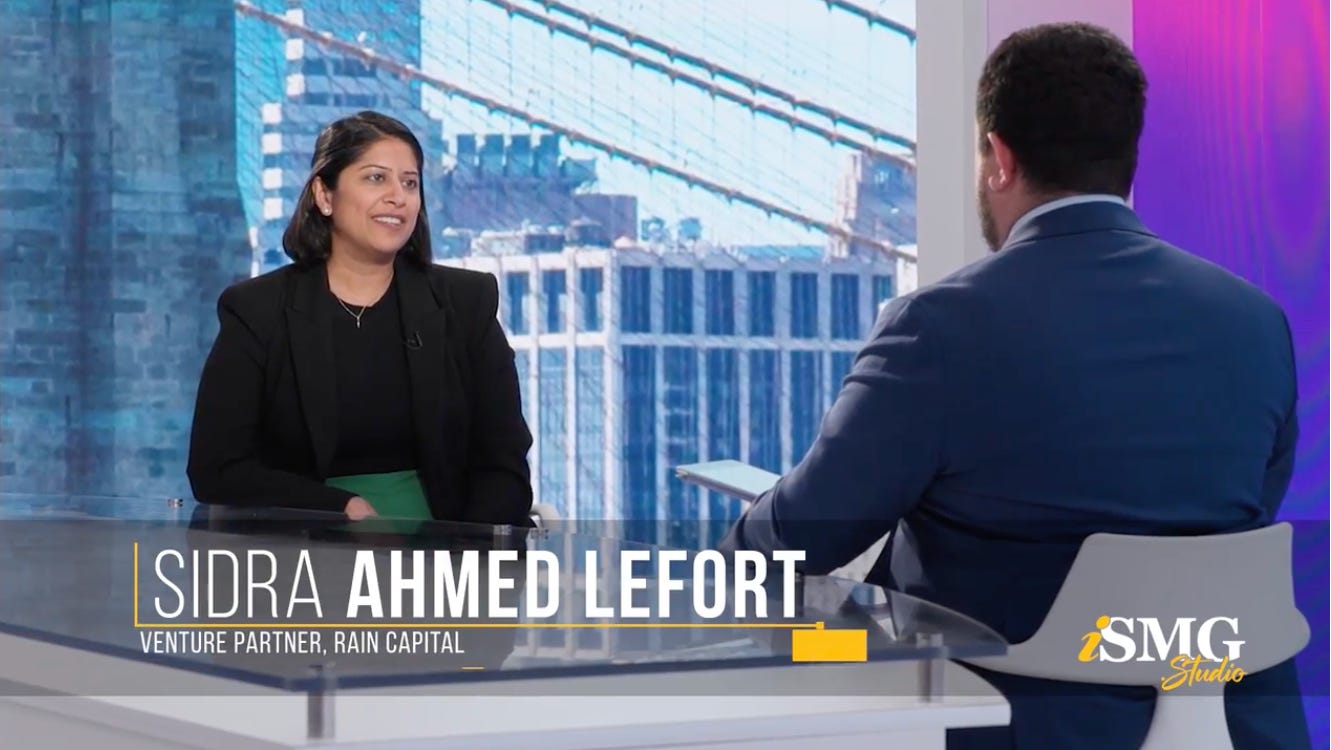
A few patterns stood out:
Capital is concentrating at the extremes
A clear barbell effect is emerging, with large seed rounds and mega-acquisitions at both ends, while Series B and C remain more constrained. This is creating real execution risk for companies in the middle.Overcapitalization can become a liability
More capital does not necessarily lead to better outcomes. When urgency fades, prioritization becomes harder and execution suffers.M&A remains the primary exit path
The pool of acquirers is expanding, particularly as infrastructure companies become more active.Second-time founders are increasingly advantaged
Experience and execution track record are commanding outsized trust and capital.
The takeaway: Capital is available, but discipline and execution matter more than ever.
Latest Podcast: Is Your AI Just “Snacking”?
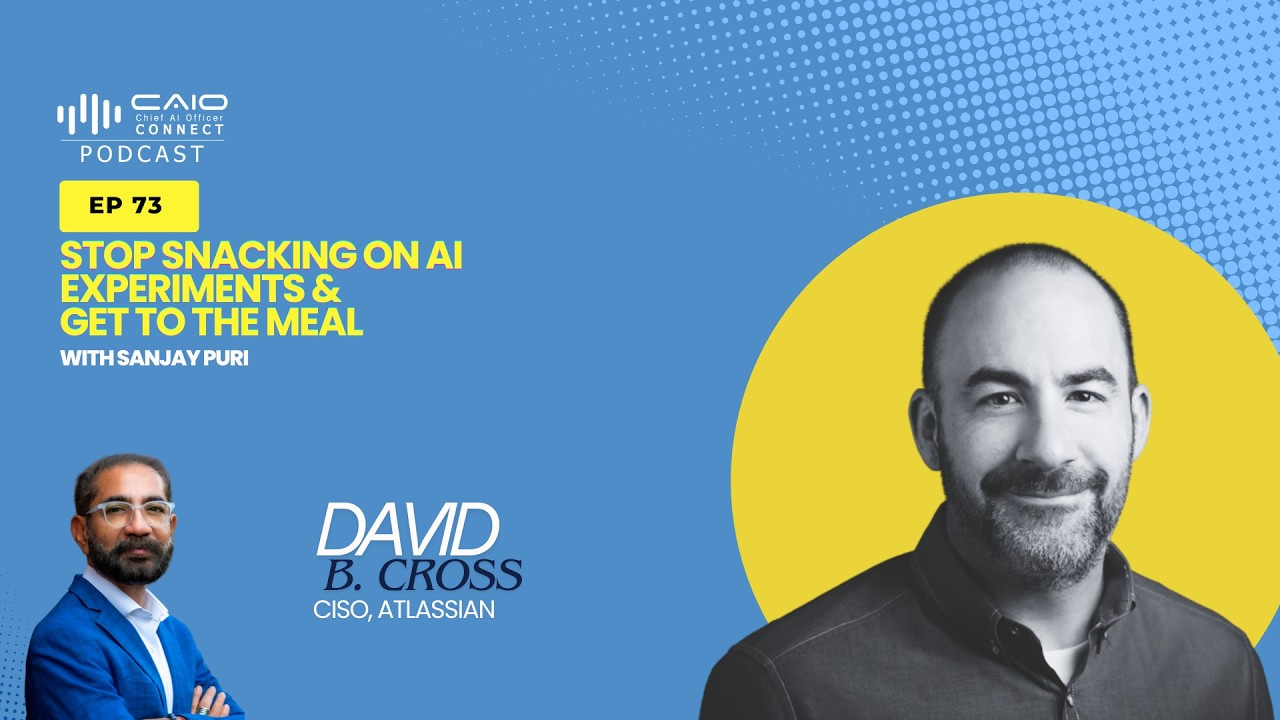
David B. Cross, Venture Partner at Rain Capital, recently shared how the current landscape marks a definitive shift from “bolted-on” AI features to truly AI-native architectures. This evolution requires moving beyond “snacking” which are minor, fragmented experiments and toward “full meals” that fundamentally transform business operations. In this new era, the security organization is no longer a rigid gatekeeper of compliance but a customer-centric engine designed to enable speed. Investors should look for organizations that can move beyond simple pilots to integrate AI into their core operational fabric, ensuring that security is a driver of enterprise productivity rather than a bottleneck.
The takeaway: The rise of autonomous agents necessitates a major overhaul of identity governance, where AI entities are treated with the same, if not more, rigor as human users. While unauthorized access remains a concern, the greater systemic risk has shifted toward massive data oversharing within internal networks. However, the defensive capabilities are keeping pace; advanced AI-driven security strategies are now capable of automatically remediating over half of the vulnerabilities found in AI-generated code. This move toward self-healing software supply chains represents the next frontier, turning security into a proactive, automated layer that protects the speed of modern innovation.

I am also writing about business study in tech. So if you have an interest in this work, please read and share your thoughts! It would be great experience. Thx and have a nice day! :)
https://fidetolabs.substack.com/p/the-6-trillion-blind-spot-why-a16z?r=2ddrtz&utm_campaign=post-expanded-share&utm_medium=post%20viewer
It’s really inspiring! Thx for sharing this nice work!